01
Regulatory and customer requirements
An ISO/IEC 27001 initiative, a NIS2 readiness question or a customer security assessment requires a defensible view of your current controls.
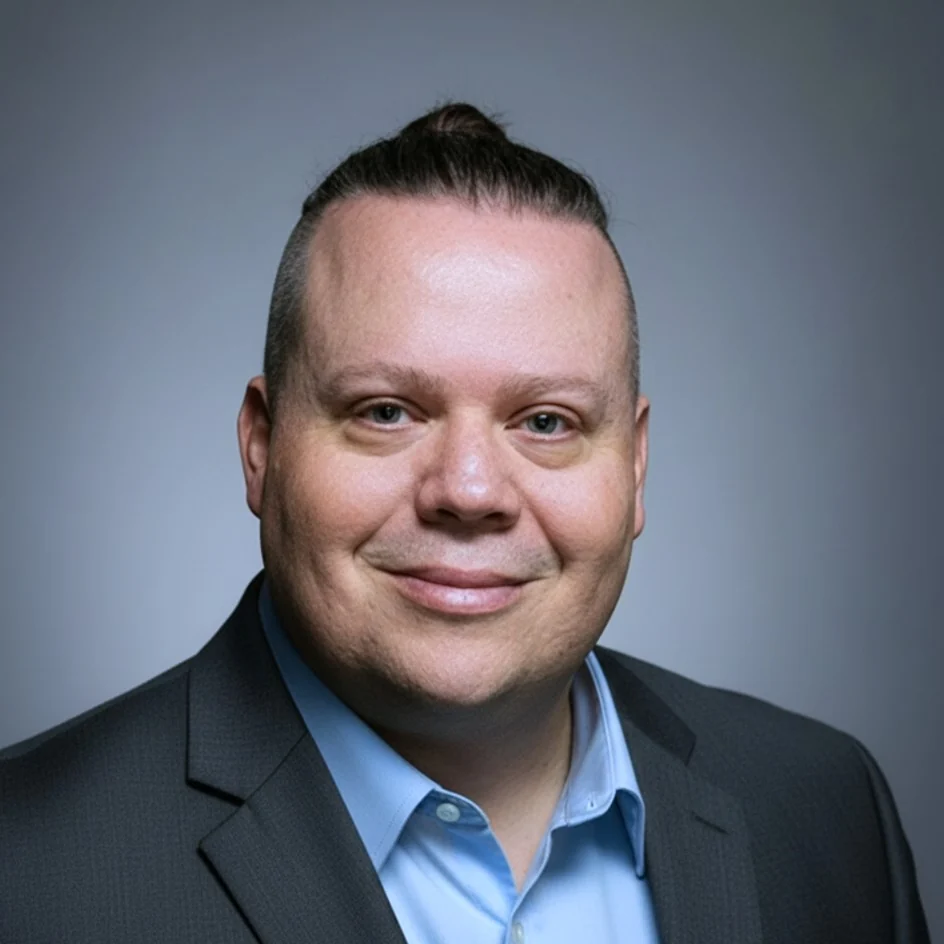
Independent consultant · Denmark
Independent advice. Practical security solutions. Business-focused decisions.
I help organizations assess and strengthen security, meet compliance requirements and implement practical controls. My work spans technical security assessments, GDPR and data protection, ISMS, IAM and security awareness. Where needed, I translate cyber risks into clear management and investment decisions.
Business needs
Engagements often begin with a need to assess security weaknesses, improve access controls, respond to regulatory or customer requirements, or make defensible security investment decisions.
01
An ISO/IEC 27001 initiative, a NIS2 readiness question or a customer security assessment requires a defensible view of your current controls.
02
Policies exist but there is limited evidence of operation, unclear accountability or unresolved gaps ahead of an internal or external review.
03
AI adoption, digital services and exposure to impersonation create decisions that need proportionate safeguards, management ownership and a practical response.
04
Vulnerabilities and inappropriate access rights need a scoped assessment, clear accountability and a practical remediation plan.
Services
Each engagement starts with an agreed scope, assumptions, evidence requirements and deliverables. The objective is a sustainable control environment—not documentation for its own sake.
01
Assess security exposure, compliance obligations and practical priorities.
I assess governance, technical controls, regulatory obligations and evidence against agreed requirements such as ISO/IEC 27001, relevant NIS2 duties, GDPR-related controls or customer assurance expectations. Where appropriate, I translate security findings into scenario-based financial exposure, mitigation options and residual risk for management decisions. Audit and certification-readiness support remains focused on documented gaps, control evidence and corrective actions.
02
Develop practical controls for security governance and access.
Establish or improve an ISMS with clear risk ownership, practical policies, control evidence and maintenance routines. Support identity and access management (IAM), including account lifecycles, access reviews and appropriate permissions.
03
Make AI use accountable, transparent and manageable.
Help organizations map AI use, establish decision rights and assess operational and regulatory exposure, including orientation to applicable EU AI Act requirements. The emphasis is on governance processes that teams can operate in practice.
04
Reduce avoidable exposure in high-trust decisions.
Review business processes in which identity claims, urgent requests or instructions can trigger payments, access changes or disclosure. Draw on payment-fraud investigation and telecommunications security-product experience to identify verification and approval improvements.
05
Examine exploitable weaknesses within an agreed, authorized scope.
Services may include vulnerability analysis, threat-informed testing and penetration testing with a written scope, named asset owners, rules of engagement and safeguards for business continuity. Findings are linked to realistic attack paths, potential blast radius, remediation priority and retesting criteria. Availability depends on engagement-specific authorization, operating conditions and insurance confirmation.
Assessment method & delivery
Risk assessment
I challenge the same issue from several opposing perspectives: an external attacker, a privileged insider, a compromised supplier or a fraud actor. These perspectives can reveal assumptions, weak controls and dependencies that a compliance checklist may miss.
A risk matrix helps structure likelihood and consequence. I then map the blast radius separately: immediate effects on identities, data and services, followed by downstream operational, financial, contractual and regulatory impact. The result is a prioritized set of controls, named owners and explicit residual-risk decisions.
Where an investment decision requires it, I estimate plausible financial consequences using a stated time horizon, incident likelihood, immediate and cascading impact, and relevant regulatory exposure. I compare these estimates with mitigation costs, expected control effectiveness and residual risk. Assumptions and uncertainty remain visible: the analysis supports decisions; it does not guarantee savings.
Agree objectives, deliverables, exclusions, evidence access and decision responsibilities before work begins.
Assess risk, operational dependencies and evidence using multiple threat perspectives; distinguish immediate impacts from cascading consequences.
Develop agreed controls, policies and management artifacts with responsible stakeholders.
Record decisions, remaining risks, accountable owners and the operating rhythm for continued maintenance.
Selected experience
Selected engagements and projects illustrate the work performed; they are not client testimonials or claims of certification.
I developed and delivered a financial-risk assessment model for a technology company, linking security scenarios, likelihood, immediate and cascading consequences, relevant compliance exposure and potential mitigation costs. The model was designed to help leadership evaluate security investment options.
Established controls applicable to GSMA SAS-UP FS.18 certification preparations, revised the internal audit plan and identified gaps and mitigation paths for audit readiness.
Owned and maintained the ISMS, including risk assessment, control development, access administration and a security-awareness program.
Remediated findings from penetration testing and developed business continuity and disaster recovery arrangements for SaaS assets.
I originated the preventive voice-call verification concept, built a working proof of concept and worked across product, engineering, security, privacy and commercial priorities, translating technical trade-offs for business leadership.
Authored and maintain AIR, an open-source framework for structured and reviewable AI-assisted work. It is not a certification or independently validated assurance service.
Investigated disputed and fraudulent card transactions and later led business support for complex cases.
Verify before committing
Compare your broad requirements with selected evidence from my professional record. The check also highlights related experience and topics that deserve clarification.
About
I hold a Professional Bachelor in IT Security and an AP Degree in IT Technology from Business Academy Aarhus. My training includes penetration-testing methods and technical security assessment. My documented work spans IAM administration, ISMS ownership, audit and certification-readiness support, vulnerability remediation, payment-fraud investigation, security-product development and AI governance.
As a security-product co-founder, I have worked across technical, compliance, operational and commercial responsibilities. I help translate the consequences of security findings into the language of budgets, business exposure and management decisions, without obscuring the underlying uncertainty.
I do not resell software, licenses or hardware. My recommendations are based on assessed risks, relevant compliance requirements and the controls an organization can operate and maintain.
Let's talk
Have a cybersecurity, risk or compliance challenge to discuss? Tell me about your priorities and the outcome you need. I will help clarify whether I am the right adviser and what a focused engagement could look like.
No obligation. The call is for an initial discussion; technical assessments and detailed recommendations are part of a separately agreed engagement. Booking takes place on Calendly; the meeting is held on Google Meet.
Mølagervej 1A
8382 Hinnerup
Denmark
Remote-first; on-site in Aarhus and East Jutland